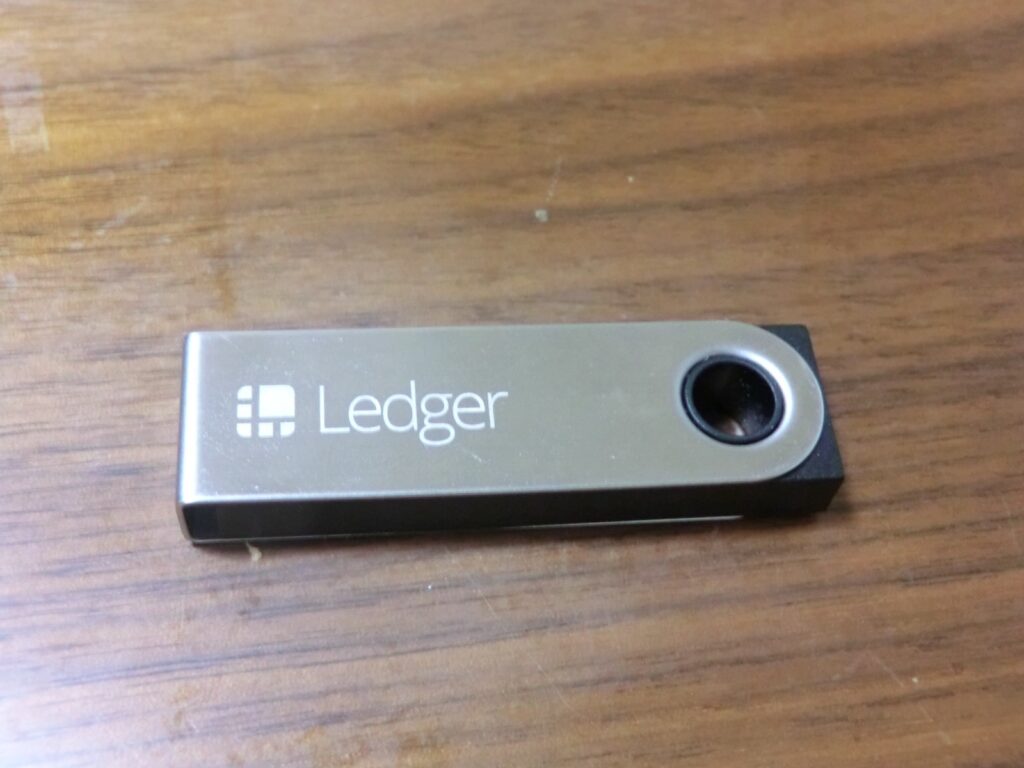
The EU’s Cyber Resilience Act (CRA) has put every company selling a crypto wallet into the European market on a 24-hour reporting clock. Since September 11, 2026, a manufacturer that becomes aware of an actively exploited vulnerability in its product must file an early warning within a day, and the duty reaches back to wallets already in users’ hands. The less obvious point is how narrow the trigger is: the Cyber Resilience Act counts flaws in the product, while most wallet losses come from phishing and stolen keys that no product flaw explains.
What the Cyber Resilience Act now requires
Article 14 of Regulation (EU) 2024/2847 sets three stages: an early warning within 24 hours of awareness, a fuller notification within 72 hours, and a final report no later than 14 days after a corrective or mitigating measure is available. Severe incidents follow the same 24-hour and 72-hour steps, with a final report due within one month. The European Commission confirms manufacturers file once, through a Single Reporting Platform, to the national Computer Security Incident Response Team (CSIRT) of their main establishment, with the information made available to ENISA.
The scope is wide. A manufacturer is anyone marketing a product with digital elements under its own name, “whether for payment, monetisation or free of charge”, so a free wallet app from a commercial company is caught like a paid hardware device. Article 69 applies the reporting duty to in-scope products placed on the market before December 11, 2027, meaning the installed base of hardware wallets and wallet apps must be reported on, not only new releases. The Act’s security-by-design requirements apply only from December 11, 2027.
How the platform and penalties work
ENISA said it had deployed the “initial operating capability” of the platform and would expand its features over the coming months. Juhan Lepassaar, Executive Director at ENISA, said: “Vulnerabilities in digital products are often exploited by threat actors to subvert or hamper critical services, such as healthcare, energy, transport or telecommunications. The streamlined reporting and sharing of information on actively exploited vulnerabilities and severe incidents helps to build a more resilient Digital Single Market.”
Crypto is not on that list, but the penalties apply regardless. Under Article 64, breaching Article 14 can bring fines of up to €15 million or 2.5% of worldwide annual turnover, whichever is higher. Micro and small enterprises cannot be fined for missing the 24-hour early-warning deadline, though the duty to report still applies. Because many self-custody wallets are built by small teams, the fines risk falls mainly on larger hardware makers and exchanges that ship their own wallet software.
Where the reporting net misses wallet losses
The data suggests the rule will capture a small share of what users lose. Chainalysis counted 158,000 personal wallet theft incidents in 2025, almost triple the 54,000 in 2022, with at least 80,000 unique victims and $713 million taken from individuals. A seed phrase handed to a phishing site is not a flaw in the wallet, so it starts no CRA clock. The regulation targets the rarer event, such as a firmware bug, compromised update or signing-library flaw, that could empty thousands of wallets at once.
For exchanges, the CRA adds a second rulebook. Crypto-asset service providers authorised under MiCA are already financial entities under the Digital Operational Resilience Act (DORA), which requires major ICT-related incidents to be reported to their financial supervisor. An exchange that also publishes a self-custody wallet is a manufacturer under the CRA, so one exploit could mean a report to a financial regulator and another to a CSIRT, on separate templates. That exposure grows as assets move off platforms: Binance said roughly 70% of its departing EEA users moved to self-custody after MiCA, and the firms that won MiCA authorisation before the transition closed have reason to build wallets to keep users. Deals such as Payward’s purchase of Magic’s embedded wallet business raise the same question of which component is the product and who its manufacturer is.
What happens next
The first test will be the first publicly known wallet exploit in the EU, where firms must show when they became aware of it, because that moment starts the clock. That should push vendors to formalise bug-bounty and threat-intelligence processes. The independent guide cyberresilienceact.eu noted that voluntary reporting and a reporting API were not part of the platform at launch, so automated security teams will file by hand for now. Open-source software stewards, which may cover some community-maintained wallets, take on reporting duties only from December 11, 2027, leaving commercial wallet brands and exchanges carrying the exposure until then.
This article is informational analysis only and is not financial, investment, or trading advice. Cryptocurrencies are highly volatile and can lose substantial value rapidly. Past performance and historical patterns do not guarantee future results. Do your own research and consult a regulated financial adviser before making any investment decision.
Karthik Subramanian
Karthik Subramanian is a founder, writer, and technology consultant with nine years in the crypto ecosystem. He covers token economics, L1/L2 infrastructure, DeFi protocols, wallets/custody, and the bridge between crypto and forex—broker technology, liquidity, and macro drivers. Karthik’s writing focuses on clear, practical frameworks that help professionals evaluate new products and on-chain innovation alongside FX market realities.
